




Exclusive High Net Worth Insurance Carriers
Our partnerships with top-tier insurance carriers allow us to offer exclusive coverage options designed specifically for high-net-worth individuals.
A Network of Specialized Advisors
Access a network of advisors who specialize in addressing your unique needs, including risk management, wealth management, and legal advice.
Policy Reviews
Ensure your coverage remains optimal and up-to-date with annual reviews of your insurance policies to address any changes in your lifestyle or assets.
Periodic Market Updates
Stay informed with regular updates on market trends and developments that could impact your insurance and risk management strategies.
Coordination of Your Team of Advisors
Benefit from coordinated efforts between your team of advisors, including attorneys, wealth managers, accountants, and insurance professionals, to ensure comprehensive protection and strategic planning.
24/7 Support
Access round-the-clock support to address any urgent needs or concerns, ensuring peace of mind at all times.
Family Office Specialty Support
Leverage specialized support tailored to family offices, including asset protection, estate planning, and succession planning.
Concierge Claim Service
Experience a seamless and hassle-free claims process with dedicated concierge claim services tailored to your needs.
Risk Management and Loss Control Insights
Receive expert insights on risk management and loss control to proactively protect your assets and minimize potential risks.

The problem is not a lack of awareness. Mid-market business owners understand that cyber incidents happen, and they know that inland flooding is the most common and most costly natural disaster in the United States. However, there is often a significant gap between that awareness and having the insurance coverage that actually responds when a loss occurs. That gap is persistent and expensive. Understanding why it exists is more useful than simply acknowledging that it does.
The Cyber Coverage Gap: What the Numbers Show
Only 38% of small and mid-sized businesses currently carry cyber insurance, according to 2026 industry data. Among those that do, a significant portion carry limits that were set before the current cost environment for cyber incidents. Today, the average cost of a ransomware incident for a mid-market company exceeds $1.2 million in total incident costs, including downtime, remediation, ransom payments, and regulatory response, according to the Ransomware Task Force’s 2026 annual report.
Three specific coverage gaps characterize the mid-market cyber exposure in 2026.
Business interruption sublimits: Standard cyber policies frequently include sublimits on business interruption coverage that are significantly lower than the total policy limit. A $2 million cyber policy with a $250,000 business interruption sublimit provides minimal protection against the income loss that typically represents the largest financial component of a ransomware incident. The sublimit is established when the policy is issued based on the underwriter’s assumptions about the average duration of a business interruption. Those assumptions often do not reflect the actual recovery timelines that mid-market companies experience when their operational systems are encrypted.
Social engineering and funds transfer fraud:Business email compromise, which involves fraudulent wire transfers initiated through impersonated executive or vendor email, generated $2.9 billion in reported losses in 2023, according to the FBI’s IC3. Standard cyber policies vary significantly in whether and how they cover funds transfer fraud. Coverage is typically written as a sublimit within the cyber policy and may require specific security controls to have been in place at the time of the loss. Businesses that have not verified how their cyber policy responds to a BEC loss, which involves a fraudulent wire transfer rather than a network intrusion, may be relying on an assumption that is not supported by their policy language.
Supply chain cyber incidents: A cyber attack that originates with a vendor, supplier, or software provider and then spreads to the insured’s systems presents a different coverage question from a direct attack. Contingent cyber coverage, which is the cyber equivalent of contingent business interruption coverage, addresses losses resulting from a cyber event at a third party whose systems the insured relies on. Very few mid-market cyber policies include meaningful contingent cyber coverage. The SolarWinds and MOVEit incidents demonstrated how extensively supply chain cyber events can affect organizations that were not the direct target.
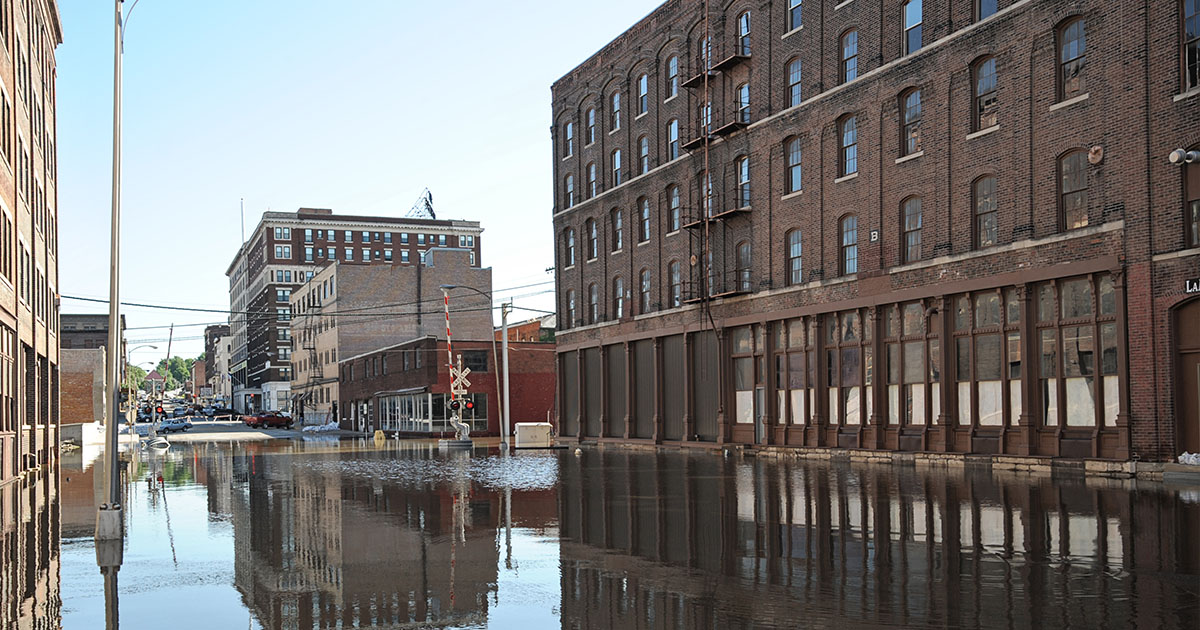
The Inland Flood Gap: Persistent and Predictable
Standard commercial property policies exclude flood coverage. This is not a surprising provision buried in the policy’s exclusion language. It is a fundamental characteristic of commercial property insurance that has been in place for decades. Flood coverage requires either a separate flood insurance policy or a specific flood endorsement to the commercial property policy. Despite this being widely understood, the commercial flood insurance take-up rate among mid-market businesses in high-risk flood zones remains below 40%, and among businesses outside designated FEMA flood zones, it falls to approximately 10 to 15%.
The designated flood zone framework is itself a coverage gap driver. FEMA’s flood maps are updated infrequently and frequently understate risk, particularly for inland flooding driven by intense rainfall events rather than coastal storm surge. A business located outside a FEMA Special Flood Hazard Area has no mandatory insurance requirement and often concludes that its flood risk is low enough to self-retain. The data does not support that conclusion. In recent major inland flood events, the majority of damaged properties were outside designated high-risk zones.
Two additional inland flood coverage questions deserve specific attention at renewal. The first is the difference between NFIP commercial coverage and private flood insurance: NFIP commercial policies cap building coverage at $500,000 and contents coverage at $500,000, with no business interruption component. Private flood markets offer higher limits, broader coverage triggers, and business income coverage that the NFIP program does not provide. The second is the waiting period: NFIP policies have a 30-day waiting period before coverage takes effect. Private market policies vary. Both waiting periods mean that flood coverage purchased after a storm is forecast provides no protection against that storm.
Why Coverage Gaps Persist Despite Awareness
Many business owners know that cyber incidents and floods can disrupt operations. Yet that awareness does not always lead to a review of their insurance coverage. Three common factors help explain why.
Optimism bias. An owner may recognize a risk in general but believe their own business is unlikely to experience it. That can make cyber or flood coverage seem less urgent than other priorities.
Renewal habits. It is easy to renew a familiar insurance program without revisiting how the business has changed. If a gap existed when the coverage was first purchased, it may carry forward year after year.
Coverage complexity. Policy terms, exclusions and limits can be difficult to assess without a careful review. Business owners may assume their property or cyber coverage addresses an exposure that the policy actually limits or excludes.
Tooher-Ferraris reviews commercial insurance programs to identify potential cyber and flood coverage gaps, compare available options and help businesses align coverage with their actual exposures. Learn more about our commercial insurance services and specialty programs.
For more information on these risks, explore the FBI’s Internet Crime Complaint Center, FEMA’s flood resources and the Insurance Information Institute.
Frequently Asked Questions
Does my commercial property policy cover flood damage?
Standard commercial property policies exclude flood coverage. A separate flood insurance policy, either through the National Flood Insurance Program or the private flood insurance market, is generally required to cover flood losses. This applies regardless of whether the property is located in a FEMA-designated flood zone.
What is the difference between NFIP commercial coverage and private flood insurance?
NFIP commercial coverage caps building coverage at $500,000 and contents at $500,000, with no business interruption coverage and a 30-day waiting period. Private flood insurance offers higher limits, broader coverage triggers, business income coverage, and in some cases shorter or no waiting periods. For businesses with property values or business interruption exposure that exceeds NFIP limits, private flood insurance provides more comprehensive protection.
What cyber coverage gaps are most commonly missed by mid-market businesses?
The three most commonly missed gaps are: business interruption sublimits that are significantly lower than the total policy limit; limited or absent social engineering and funds transfer fraud coverage; and the absence of contingent cyber coverage for losses caused by incidents at vendors or suppliers. Each of these should be specifically confirmed with the broker rather than assumed to be included.
Ready to review your cyber and flood coverage gaps? The team at Tooher-Ferraris has been helping businesses identify and close coverage gaps since 1932. Contact us today to schedule a no-obligation consultation — https://toofer.com/contact-us/
Q4 is when ACA compliance failures become expensive. The fourth quarter is the deadline window for year-end compliance actions, and it is also when HR teams are most stretched, managing open enrollment, processing plan changes, and supporting employees through benefits decisions while closing out the plan year’s administrative obligations. Compliance items that get deferred in September and October have a habit of becoming enforcement problems in January. Here are seven ACA compliance items every mid-sized employer should complete before December 31, 2026.
1. Verify Your Plan Meets the 2026 ACA Affordability Threshold
The ACA requires applicable large employers (those with 50 or more full-time equivalent employees) to offer coverage that is affordable to full-time employees. For plan years beginning January 1, 2026, the affordability threshold is 9.02% of household income. Coverage is affordable if the employee’s required contribution for the lowest-cost, minimum-value plan option does not exceed 9.02% of the federal poverty level for a single individual.
Employers who have adjusted plan contributions since their last affordability analysis, or who have not recalculated since the threshold changed, should verify that their current contribution structure satisfies the 2026 threshold. An employer whose plan fails the affordability test and who has full-time employees who purchase subsidized coverage through the ACA marketplace may be subject to the employer shared responsibility payment, which for 2026 is $4,020 per full-time employee who receives a subsidy (excluding the first 30 employees).
2. Update HSA Contribution Limits in Payroll and Plan Communications
The IRS increased HSA contribution limits for 2026 to $4,400 for individual coverage and $8,750 for family coverage, with a $1,000 catch-up contribution available for participants age 55 and older. Employers who administer HSA programs through payroll deduction must update their payroll systems to reflect the new limits. More commonly missed: employee communications, enrollment materials, and benefits administration platforms that still display 2025 limits need to be updated before open enrollment closes.
High-deductible health plan (HDHP) minimum deductible and out-of-pocket maximum limits have also been adjusted for 2026. HDHP minimum deductibles are $1,650 for self-only coverage and $3,300 for family coverage. Out-of-pocket maximums are $8,300 for self-only and $16,600 for family. Plans that do not meet these thresholds cannot be paired with an HSA, which means employees enrolled in what they believe to be an HSA-compatible plan may be ineligible to contribute to their HSA if the plan design has not been updated.
3. Confirm Electronic Filing Requirements Are Met
The IRS now requires electronic filing for employers submitting 10 or more information returns, including Forms 1094-C and 1095-C. Employers who previously filed on paper because they were below the old 250-return threshold should confirm their 2026 filing approach and ensure they have access to an IRS-approved electronic filing system or are working with an ACA reporting vendor who files electronically on their behalf. Paper filings from employers required to file electronically are treated as late filings.
4. Audit Machine-Readable Files for Transparency in Coverage
The Transparency in Coverage rules require most non-grandfathered group health plans to make machine-readable files containing in-network rates and out-of-network allowed amounts publicly available. The files must be updated monthly and accessible without registration or login. Employers should confirm that their carrier or third-party administrator is maintaining the files and that the public link works.
5. Complete Nondiscrimination Testing for 401(k) and Cafeteria Plans
Section 125 cafeteria plans and 401(k) plans have nondiscrimination requirements designed to prevent benefits from disproportionately favoring certain employees. The tests and definitions differ by plan type, so employers should review each plan separately. For 2026 retirement plan testing, the highly compensated employee compensation threshold remains $160,000. Employers whose workforce or benefit elections have changed should arrange testing in time to evaluate any needed corrections.
The appropriate correction depends on the plan and the test that failed. Reviewing results before year end may give employers more options to address a potential failure.
6. Prepare COBRA Administration Records for Year-End Review
Year end is a useful time to audit COBRA records. Confirm that qualifying events were reported, election notices were sent, elections were administered and premium payment records are current. Generally, an employer has 30 days to notify the plan administrator of certain qualifying events, and the plan administrator has 14 days after receiving that notice to send an election notice. Different timing can apply when the employer is also the plan administrator. The Department of Labor’s COBRA guide for employers explains these responsibilities.
7. Update Plan Documents and Summary Plan Descriptions
Review plan documents and summary plan descriptions (SPDs) against the changes planned for January 1, 2027. Under ERISA, an updated SPD or summary of material modifications (SMM) generally must be furnished within 210 days after the end of the plan year in which a material change was adopted. Shorter notice rules can apply to certain reductions in health benefits or changes affecting a summary of benefits and coverage. Employers should coordinate the required notices with their open enrollment materials and plan documents.
Tooher-Ferraris helps employers navigate ACA compliance obligations, review benefit plan design and coordinate with ERISA counsel on documentation requirements. Learn more about our HR compliance and legal resources and employee benefits strategy and consulting services.
For additional guidance, visit the IRS retirement plans resources and the Department of Labor’s Employee Benefits Security Administration.
Ready to complete your year-end ACA compliance checklist? The team at Tooher-Ferraris has been helping employers navigate benefits compliance since 1932. Contact us today to schedule a no-obligation consultation — https://toofer.com/contact-us/
Frequently Asked Questions
What is the ACA affordability threshold for 2026?
The ACA affordability threshold for plan years beginning January 1, 2026 is 9.02% of household income. Coverage is considered affordable if the employee’s required contribution for the lowest-cost, minimum-value single plan option does not exceed 9.02% of the applicable federal poverty level for a single individual. Applicable large employers whose plans fail this threshold and who have full-time employees purchasing subsidized marketplace coverage may be subject to employer shared responsibility payments.
What are the 2026 HSA contribution limits?
The IRS increased HSA contribution limits for 2026 to $4,400 for self-only coverage and $8,750 for family coverage. The catch-up contribution limit for participants age 55 and older remains $1,000. HSA-compatible HDHP minimum deductibles are $1,650 for self-only and $3,300 for family, with out-of-pocket maximums of $8,300 and $16,600 respectively.
Which employers are required to file ACA information returns electronically?
Employers filing 10 or more information returns, including Forms 1094-C and 1095-C, are required to file electronically with the IRS. This threshold was reduced from 250 returns in prior years. Employers who previously filed on paper should confirm whether they now exceed the 10-return threshold and arrange electronic filing through an IRS-approved system or ACA reporting vendor.
Mental health parity compliance is the employee benefits compliance issue most likely to generate enforcement action against a mid-sized employer in the fourth quarter of 2026 and most employers are not prepared for it. The Mental Health Parity and Addiction Equity Act requires that the limitations placed on mental health and substance use disorder benefits be no more restrictive than those placed on medical and surgical benefits. The 2026 plan year brings full documentation requirements into force, and the Department of Labor has elevated scrutiny of employer compliance as a specific enforcement priority.
The enforcement mechanism that makes this particularly urgent is the DOL’s authority to request a plan’s comparative analysis at any time, without advance notice and without a specific complaint triggering the request. An employer that cannot produce a compliant comparative analysis within 45 days of a DOL request is subject to enforcement action. According to compliance guidance published in 2026, the majority of employer-sponsored plans that have been reviewed by the DOL have required remediation. Here are five things every employer must know and act on before December 31.
1. Understand What the Comparative Analysis Actually Requires
The non-quantitative treatment limitation (NQTL) comparative analysis is a detailed, written document that compares the factors, evidentiary standards, and processes used to determine mental health and substance use disorder benefit limitations against those used for medical and surgical benefits. It is not a summary. It is not a checkbox. It requires a specific, reasoned explanation of each NQTL applied to mental health benefits, the comparable limitation applied to medical/surgical benefits, and the basis for concluding that the limitations are equivalent.
NQTLs include prior authorization requirements, step therapy protocols, network admission standards, reimbursement rate methodologies, and fail-first requirements. Each of these must be evaluated and documented on both the mental health and medical/surgical side of the plan. The analysis must be plan-specific. A generic template from a carrier or TPA does not satisfy the requirement unless it is customized to the specific plan’s design and the specific limitations in place.
2. Know Who Is Responsible for Producing It
For fully insured plans, the insurance carrier is required to conduct and provide the comparative analysis to the plan sponsor upon request. The employer’s obligation is to request it from the carrier, review it for completeness, and retain it. “My carrier handles compliance” is not a valid response to a DOL request. The plan sponsor remains responsible for ensuring that a compliant analysis exists and can be produced.
For self-funded plans, the employer or the third-party administrator is responsible for producing the analysis. TPAs vary significantly in the quality and completeness of the comparative analysis documentation they provide. An employer whose TPA has provided a generic template rather than a plan-specific analysis may believe they are compliant when they are not. Reviewing the analysis with qualified ERISA counsel before a DOL request arrives is the only way to know whether the documentation would survive scrutiny.
3. Understand What Non-Compliance Actually Costs
An employer that receives a DOL request for a comparative analysis and cannot produce one within 45 days must notify plan participants that the plan is not in compliance with MHPAEA. This is more than a theoretical consequence. It can create reputational risk, potential litigation from plan participants who were denied mental health benefits that would have been available under a compliant plan, and continued DOL enforcement activity until compliance is achieved.
Litigation risk from plan participants is a less-publicized but potentially more financially significant consequence of MHPAEA non-compliance. Employees who were denied mental health benefits, or who were required to pay higher out-of-pocket costs than they would have for comparable medical benefits, may have a private right of action under ERISA. Courts have permitted retrospective benefit claims in some cases, meaning non-compliance identified in 2026 could result in liability for benefits that were improperly denied in prior plan years.
4. Complete These Three Actions Before Year End
Request the comparative analyses in writing. Ask your carrier or third-party administrator (TPA) for the plan’s documented analyses of its nonquantitative treatment limitations, such as prior authorization and provider network standards. Keep the request, the response and any follow-up questions. If the materials do not address your plan’s practices, identify what is missing and ask how it will be supplied. Federal law continues to require these analyses even though the Departments have paused enforcement of the new provisions in the 2024 MHPAEA final rule. U.S. Department of Labor
Have qualified ERISA counsel review the materials. Counsel can assess whether the analyses address the plan’s actual limitations, identify missing information and advise on the requirements that currently apply. This is particularly useful while the Departments reconsider the 2024 final rule. U.S. Department of Labor
Examine access to mental health providers. Ask for evidence about the plan’s network standards and members’ ability to obtain care, including whether listed providers accept new patients and how long members wait for appointments. Compare relevant mental health and substance use disorder access measures with medical and surgical access, and have counsel advise how the findings should be addressed in the applicable comparative analyses. The DOL’s MHPAEA self-compliance tool provides a starting point for this review. dol.gov
5. Prepare for the 2027 Plan Year Now
MHPAEA compliance is an ongoing responsibility. Use the fourth quarter of 2026 to obtain the analyses, resolve missing information and set a process for reviewing plan changes and network practices in 2027. The Departments’ current enforcement statement makes an important distinction: the pause applies to new provisions of the 2024 final rule, while MHPAEA’s statutory obligations, including the comparative analysis requirement, remain in effect. U.S. Department of Labor
Tooher-Ferraris can help employers organize a benefits compliance review and coordinate with the appropriate advisers. Explore our HR compliance and legal support and employee benefits strategy and consulting services.
Ready to review your plan’s MHPAEA documentation? Contact Tooher-Ferraris to schedule a consultation.
Frequently Asked Questions
What is an NQTL comparative analysis and who is required to have one?
A non-quantitative treatment limitation comparative analysis is a written document required under MHPAEA that compares the limitations placed on mental health and substance use disorder benefits against comparable limitations on medical and surgical benefits. All employer-sponsored group health plans that offer both medical and mental health benefits are required to have a current, plan-specific comparative analysis available for DOL review.
How quickly must an employer respond to a DOL request for an MHPAEA comparative analysis?
Employers have 45 business days to respond to a DOL request with a compliant comparative analysis. If the plan cannot produce one within that period, the employer must notify plan participants of the non-compliance. The DOL may then require corrective action and continue enforcement until a compliant analysis is in place.
What happens if our plan is found non-compliant with MHPAEA?
Consequences include mandatory participant notification, DOL-required corrective action, potential plan disqualification, and private litigation from plan participants who were denied benefits under non-compliant plan terms. Courts have allowed retrospective benefit claims, creating liability for prior-year benefit denials that resulted from non-compliant NQTL applications.